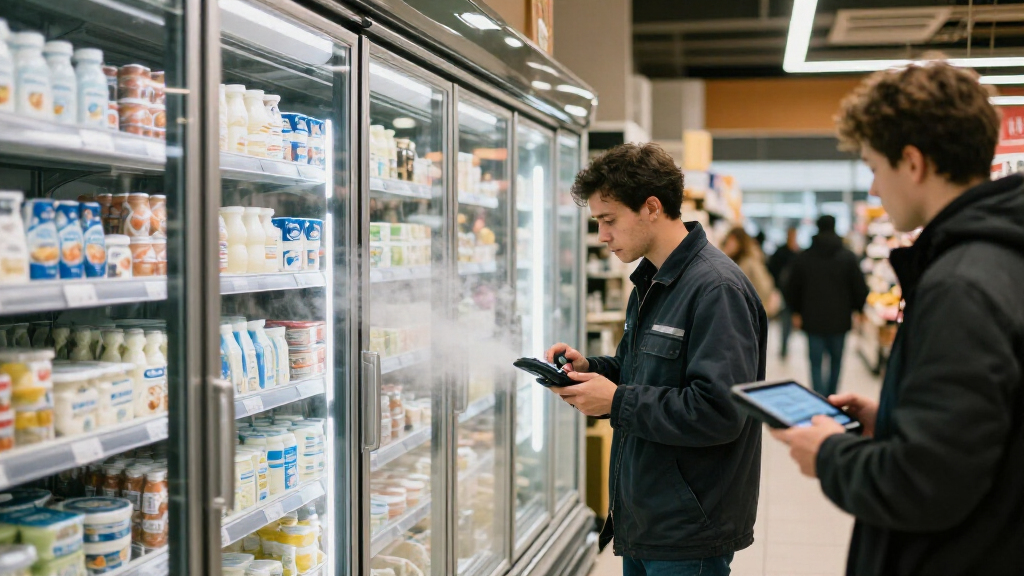
🔍 Read the full analysis: Is AI Part Of The Growing Threat To European Supermarket Refrigeration? on ThorstenMeyerAI.com

Prime made for students and young adults
- Fast, free delivery for dorm and study essentials
- Prime Video and Amazon Music included
- Member-only deals
TL;DR
A cyber incident disrupted refrigeration at more than 115 supermarkets and other food businesses across at least six European countries overnight on November 1–2, according to reports. The method appears to match an October attack in France, but officials have not identified who was responsible or found evidence that AI was used.
Cyberattacks disrupted refrigeration systems at more than 115 European stores and food businesses overnight on November 1–2, according to media and company reports, with affected sites in at least six countries. The incident appears to use the same remote-access method reported in France in October, but no attacker has been identified and authorities have not confirmed any role for artificial intelligence.
Reports name Belgium, the Netherlands, Sweden, Luxembourg, Ireland and Estonia among the affected countries; Finnish authorities and retailer Kesko also reported temperature problems at a few smaller stores in Finland. The precise total remains unsettled because outlets and authorities have published different counts. BleepingComputer reported more than 115 affected sites, while The Record reported more than 50 in Belgium alone.
In Belgium, Ahold Delhaize said an IT incident affected refrigeration systems at several dozen stores. Carrefour Belgium reported 15 affected stores out of 700, while Colruyt said about five independently operated Spar stores were affected and its own stores were not. Coop in Sweden reported problems at seven of its more than 800 stores; ICA said at least four affected stores operated outside its central network. Reports also included 13 SuperValu stores in Ireland, one Selver store in Estonia, and at least 17 businesses in the Netherlands, mostly butchers and neighbourhood shops, according to a Danfoss spokesperson quoted by NOS.
Belgian installer Sabcobel’s chief executive, Stephan Moelans, told Belgian media that technicians began disconnecting installations at about 1 a.m. He said roughly 20 of the several hundred installations his company manages in Belgium were affected and described the mechanism as the same as in France: refrigeration evaporators were remotely switched into defrost mode. In some locations, temperatures rose enough to spoil food. A Proxy Delhaize store in Hoepertingen estimated a loss of at least €60,000 in discarded food, according to local reporting cited by VRT NWS. Other businesses reported damage, while some stopped systems in time.
European retail cyber incident · November 2026
Is AI Part of the Growing Threat to European Supermarket Refrigeration?
A reported overnight cyber incident disrupted refrigeration at more than 115 stores and food businesses across Europe. Reports point to remotely altered controllers; who was responsible—and whether AI played any role—remains unconfirmed.
01 / The incident
A cold chain disrupted overnight
Reports describe refrigeration controllers being remotely changed, with some evaporators switched into defrost mode. The exact access route and the final number of affected businesses remain unclear.
BleepingComputer reported more than 115 affected sites. The Record separately reported more than 50 in Belgium alone. Counts vary by outlet and may refer to different kinds of sites.
Food at risk
Some locations saw temperatures rise enough to spoil food. A Proxy Delhaize store in Hoepertingen estimated at least €60,000 in discarded stock, according to local reporting cited by VRT NWS.
Systems disconnected
Belgian installer Sabcobel said technicians began disconnecting installations at about 1 a.m. Its CEO reported roughly 20 affected installations among several hundred it manages in Belgium.
02 / How the disruption may have unfolded
From remote access to food loss
The reported mechanism resembles the October incident in France. Public reporting has not established the precise route into the controllers.
Controller reachable
Remote-management interfaces for refrigeration equipment were reportedly exposed online.
Settings altered
Installations were reportedly switched into defrost mode, changing normal cooling operation.
Temperatures rise
Some stores reported elevated temperatures; the extent varied from site to site.
Checks and losses
Businesses disconnected or inspected systems; some reported spoiled stock and financial damage.
03 / A reported second wave
France in October, Europe in November
The sequence has prompted questions about whether incidents share an operator. Similar reported methods do not by themselves establish common responsibility.
France
Cyberattacks disrupted refrigeration systems. The Paris prosecutor’s office counted about 700 victims, according to the source material. On October 12, CERT-FR warned that remote-management interfaces were exposed online contrary to good practice and said campaigns were probably ongoing.
Multiple European countries
Reports described a new overnight disruption across supermarkets and other food businesses. Belgian authorities opened a criminal investigation; no suspect or group has been publicly named.
“We have identified an IT incident affecting the refrigeration systems in several dozen stores.”
Ahold Delhaize · company statement
04 / Attribution and AI evidence
What is known—and what is not
A broader warning about AI-related cyber risks is separate from evidence about this incident. Reports have not established AI use in finding controllers, gaining access, or changing settings.
Investigation underway
Belgium’s federal prosecutor has opened a criminal investigation. Retailers and refrigeration specialists are checking systems and restoring operations. Public reports point to exposed remote-management interfaces as a security concern, while the exact access route remains unconfirmed.
AI, identity, total damage
No suspect, group, motive, or claim of responsibility has been made public. AI involvement is unconfirmed. The final site count, combined financial losses, and whether every report concerns the same actor are also unknown.
“Currently 15 of our 700 stores are affected, both in Flanders and Wallonia.”
Carrefour Belgium · company statement05 / Key questions
What readers should take away
What happened to the refrigeration systems?
Reports say attackers remotely changed controller settings, causing some units to enter defrost or heating modes. The exact access route has not been publicly confirmed.
How many stores were affected?
One report counted more than 115 sites across at least six countries; Finnish sources also described problems at a few smaller stores. The final total is unknown.
Has anyone confirmed AI was used?
No. A general warning about AI-related cyber risks does not establish that AI was used in these attacks. AI-generated imagery or voice in a video is not evidence about the attack method.
Who carried out the attacks?
No suspect or group has been publicly identified, and no one has claimed responsibility. Belgium’s federal prosecutor has opened an investigation.
Were all affected stores part of major chains?
No. Reports include independent businesses and outlets using separate refrigeration systems, as well as chain stores. Some retailers said affected sites operated outside central networks.
Why does the incident matter?
Internet-connected building systems can affect everyday retail operations. A change to refrigeration controls can put perishable food, store finances, and supply continuity at risk.
Food Losses and Exposed Store Systems
The disruption shows how an online-accessible building system can affect ordinary retail operations, not just data or payment services. When refrigeration controls are changed, perishable food can become unsafe or unsellable, creating direct costs for individual shops and potential supply and waste consequences. The reported losses vary by location, and there is no consolidated estimate of the total damage.
The pattern reported by retailers also points to uneven protection. Several affected outlets were independently operated, outside a chain’s central network, or using separate refrigeration equipment. That does not establish that smaller stores are inherently less secure, but it highlights how equipment outside central safeguards may be harder for a parent company to monitor and manage. The incident is relevant to businesses that connect refrigeration and other building controls to the internet.
Products Worth Considering

Samsung 32-inch Odyssey OLED G8 (G80SH) 4K QD-OLED Gaming Monitor

Samsung 49-Inch Odyssey G93SC QD-OLED Curved Gaming Monitor

LG UltraGear 34GX90SA-W 34-inch WQHD Curved OLED Gaming Monitor
As an affiliate, we earn on qualifying purchases.
A Second Reported Wave Since October
The November incident followed attacks on refrigeration systems in France during the night of October 11–12. The Paris prosecutor’s office counted about 700 victims in that episode, according to the source material. France’s national cybersecurity agency, CERT-FR, warned on October 12 that remote-management interfaces for refrigeration controllers were exposed online contrary to good practice, and said campaigns were probably still ongoing.
The Belgian cyber centre has warned more broadly about a rise in cyberattacks that can involve AI. That general warning is separate from evidence about this incident: no cited company or authority has said AI was used to find the controllers, gain access or alter settings. The source material also describes a video about the incident as using AI-generated images and an AI voice clone for narration; that production choice is not evidence that AI was part of the attacks.
““We have identified an IT incident affecting the refrigeration systems in several dozen stores.””
— Ahold Delhaize
Attribution and AI Evidence Remain Unknown
Authorities have not publicly named a suspect, group or motive, and there has been no claim of responsibility. Belgium’s federal prosecutor has opened a criminal investigation. The Belgian cyber centre has warned that the attacker may never be identified.
The number of affected businesses is also not final: reports differ by country and retailer, and some describe stores while others count businesses or installations. Reported temperatures range from around 15°C in one Belgian store to 50°C in Eeklo and some other locations. It is not clear how many sites lost food, what the combined financial losses are, or whether every reported incident came from the same actor. AI involvement is unconfirmed; no evidence cited in the reports establishes that AI was used.
Investigators Trace the Remote Access
Belgian investigators are examining the incident, while affected retailers and refrigeration specialists are working to restore and check systems. The key questions are how the internet-reachable controllers were accessed, whether the October and November incidents share an operator, and how many sites were affected in total. Companies have not announced a final accounting of losses or a common remediation plan.
For now, the incident reports point to exposed remote-management interfaces as a security concern, but the exact access route and the extent of any remaining exposure are not established publicly. Further updates from prosecutors, national cybersecurity agencies, retailers and equipment providers may clarify the attribution, the number of affected businesses and whether additional safeguards have been put in place.
Key Questions
What happened to the supermarket refrigeration systems?
Reports say attackers remotely changed settings on refrigeration controllers, causing some units to enter defrost or heating modes. The exact access route has not been publicly confirmed.How many stores were affected?
BleepingComputer reported more than 115 sites across at least six countries, and Finnish sources also described problems at a few smaller stores. Counts differ among reports and may refer to different types of sites, so the final total is unknown.Has anyone confirmed that AI was used?
No. Officials and companies have not said AI was involved in these attacks. A broader warning about AI-related cyber risks does not establish AI use in this incident.Who carried out the attacks?
No suspect or group has been publicly identified, and no one has claimed responsibility. Belgium’s federal prosecutor has opened an investigation.Were all affected stores part of major supermarket chains?
No. Reports include chain stores as well as independent businesses and outlets using separate refrigeration systems. Several retailers said affected stores operated outside their central networks or safeguards.Source: ThorstenMeyerAI.com