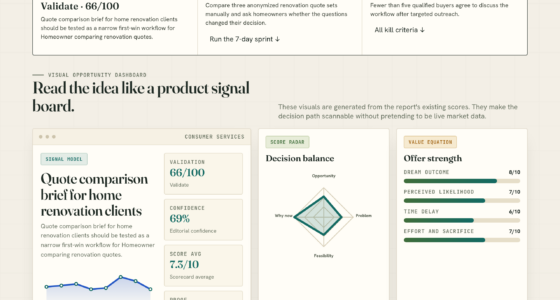
📊 Full opportunity report: Why Agent Security Starts With Action-Level Approval on IdeaNavigator AI — validation score, market gap, and execution plan.

Prime made for students and young adults
- Fast, free delivery for dorm and study essentials
- Prime Video and Amazon Music included
- Member-only deals
TL;DR

A proposed security workflow would place a proxy between an autonomous AI agent and a high-risk API, requiring a signed, single-use token for each action and its arguments. The proposal is an MVP to test, not a reported deployment or proven security product; its effects on unsafe actions and latency remain unmeasured.
IdeaNavigator AI has proposed a narrow security workflow for autonomous AI agents: put a proxy between an agent and a high-risk API, then require a signed, single-use authorization for each action and its arguments. The concept targets platform engineers whose agents can perform real-world tasks, such as issuing refunds or deleting records, but is a proposed MVP—not a reported product launch or validated result.
In its proposal, IdeaNavigator AI identifies a specific access-control risk: teams may give agents broad API tokens that allow multiple operations, so a prompt-injection attack or a reasoning mistake could trigger an action without approval scoped to that request. The proposal lists sending refunds, deleting records and emailing customers as examples of potential consequences, not documented incidents.
IdeaNavigator AI’s proposed design has an agent request a token describing the exact action and arguments. A proxy would check the request against policy rules, issue a signed token for one use if approved, and record both grants and denials for review. The proposal recommends initially placing the proxy in front of one high-risk API, rather than trying to govern every agent tool at once.
IdeaNavigator AI suggests testing the workflow around a team’s refund or delete endpoint for one month. The proposed evaluation would compare blocked unsafe actions and added latency against the team’s unscoped baseline. The proposal also suggests charging per authorized action, alongside a platform fee for policy controls and an audit dashboard. It reports no pricing, implementation results or customer trial.
Why Broad Agent Tokens Matter
IdeaNavigator AI’s proposed design shifts authorization from a standing permission to a decision made for each action. That could give platform teams a chance to reject or inspect a risky request before it reaches a business system, while creating a record of what was allowed or denied. The proposal says an audit trail could help teams review agent behavior after an unexpected result.
The practical trade-off is between control and speed. A proxy introduces an additional step for each protected request, and policies must describe which actions and arguments are acceptable. IdeaNavigator AI proposes a month-long test to measure added latency alongside blocked unsafe actions; without those results, it is not possible to say whether the controls would reduce risk enough to justify operational overhead.
For readers evaluating agent deployments, the proposal illustrates how approval can be scoped more narrowly than a general API credential. However, a token tied to one request does not by itself establish that the request is safe, that the agent’s inputs are trustworthy, or that the policy is correctly configured. Those questions depend on the system’s implementation and testing.
Products Worth Considering

Bose S1 Pro+ Portable PA Speaker

Jackery Solar Generator 1000 v2 with 200W Solar Panel

Logitech MX Master 4 for Mac, Ergonomic Bluetooth Mouse with Haptic Feedback, Ultra-Fast Scrolling, USB-C Charging, for MacOS, iPadOS, Windo
As an affiliate, we earn on qualifying purchases.
From Standing Access to Single Actions
IdeaNavigator AI frames its proposal around a change in how software agents are used: frameworks can call tools and perform actions outside a chat interface. When those tools connect to systems that handle payments, customer records or communications, an agent’s permissions can have direct operational effects.
The company argues that conventional OAuth scopes can be coarse for this use case: they may grant standing access to a category of operations instead of authorizing one action for a limited period. Its proposed proxy would add a separate, per-action decision layer. This is a design recommendation, not evidence that all OAuth configurations lack adequate controls or that the approach is already in production.
IdeaNavigator AI suggests a deliberately limited first test: protect a single refund or deletion endpoint for one team, then compare outcomes with the team’s existing unscoped setup. That scope makes the concept easier to evaluate than a broad, organization-wide rollout, but results from one endpoint would not establish how well it works across other tools or workflows.
Evidence Still Needed From a Pilot
IdeaNavigator AI provides no pilot findings. Its proposal does not say whether the proxy has been built or deployed, how much latency it would add, how often it would block unsafe actions, or how frequently it might interrupt legitimate work. It also provides no baseline measurement, customer feedback, security assessment or pricing data.
Other implementation details remain open: how the proxy would verify and protect signing keys, prevent token reuse, handle retries, and respond if the authorization service is unavailable. The proposal calls for signed, single-use tokens and policy checks but does not specify the technical design. It also does not establish how the system would identify an unsafe action or prevent harm caused by a request that passes the policy checks.
As a result, the idea should be read as a testable product concept, not as proof that action-level approval prevents prompt injection or makes autonomous agents safe. Its effectiveness would depend on the policies, integrations and safeguards used in a real deployment.
A One-Month Endpoint Test
IdeaNavigator AI proposes placing one team’s refund or deletion endpoint behind the proxy for a month. During that period, the team would require per-action tokens and compare blocked unsafe requests and added latency with an unscoped baseline. A useful report would also clarify how unsafe actions were defined, whether legitimate actions were denied, and how the audit records were reviewed.
The proposal names no team or start date and reports no pilot results. Until those details are available, the next meaningful development would be evidence from an actual test, including operational costs and the limits of the controls—not simply a description of the proposed architecture.
Source: IdeaNavigator AI proposal
Key Questions
What is action-level approval for an AI agent?
It is a proposed approach in which an agent must obtain authorization for a specific action and its arguments, rather than relying only on broad, standing API access.
How would the proposed proxy work?
The proxy would sit between the agent and a high-risk API, check each request against policy, and issue a signed, single-use token for approved actions. It would log approvals and denials.
Has this workflow been shown to prevent unsafe actions?
No results are provided. The concept proposes measuring blocked unsafe actions in a pilot, but it does not report a completed test or establish that the workflow prevents prompt injection or other failures.
What would a pilot measure?
The suggested test would wrap one team’s refund or delete endpoint for one month and compare blocked unsafe actions and added latency with an unscoped baseline. No pilot team or results are named.
Source: IdeaNavigator AI